Protect cash flow and supplier relationships with managed email security, clear payment verification, and a response plan your team can use with Gamma’s help.
A fraudulent payment-change email can leave your business short of cash while a supplier still expects payment. Treat every change to payment instructions as a separate approval decision, verify it through an established contact, and bring suspicious messages to Gamma for investigation.
Gamma’s managed IT and cybersecurity services give your business a team responsible for agreed email protections, account security, monitoring, and response. Your finance team keeps control of payment approval, with a clear route to expert help when a request looks questionable.
Why a convincing email can still put your money at risk
Business email compromise, often shortened to BEC, is a scam that uses a trusted business identity to influence a payment or obtain information. A criminal may impersonate a supplier or executive, or use a stolen email account to join an existing conversation. The FTC’s business email guidance explains how impersonation can be used to obtain money or sensitive information.
A supplier’s normal writing style, signature, or invoice format can make a request feel familiar. An existing thread needs the same payment checks as a new message, because someone with mailbox access may have read the earlier correspondence.
Hypothetical example: a supplier emails revised bank details while your team is finishing a busy payment run. The important decision is whether your business has independently confirmed the change, and Gamma can investigate the message while your finance team pauses the update.
What Gamma manages behind the email
Email protection involves several jobs that need ongoing attention. Gamma manages the agreed protections, checks security signals, and investigates suspicious activity so your staff have an expert team carrying the technical work.
Email authentication helps receiving systems check whether a message claiming your domain came through authorized sending systems. A domain is the part of an email address after the @ symbol. SPF identifies authorized sending servers, DKIM adds a verifiable digital signature, and DMARC connects authentication to the visible sender domain and a handling policy.
Gamma can review those settings alongside the services your business uses to send email, such as its website and billing platform. Changes need care because legitimate messages also depend on correct configuration. Microsoft’s email authentication documentation explains the mechanisms and their relationship to spoofing protection.
A message from a genuinely compromised account can still come through that account’s normal email system. Payment authorization therefore needs its own verification step, even after an email passes technical checks.
| Business concern | Gamma’s technical responsibility within the agreed service | Your team’s payment decision |
|---|---|---|
| A message appears to use your company’s identity. | Review domain authentication and email protection settings, then investigate suspicious messages. | Confirm the request through the established approval process. |
| Someone gains access to an employee’s mailbox. | Manage agreed account protections, investigate alerts, and contain confirmed compromise. | Pause affected payment changes and verify relevant conversations. |
| A supplier asks for new payment details. | Examine the suspicious message and signs of account misuse. | Confirm the change through a known contact before approval. |
| Employees need practice spotting suspicious requests. | Manage agreed BullPhish ID training and phishing exercises, review results, and follow up on learning gaps. | Apply the same verification and approval steps during everyday payment work. |
The exact tools, features, training schedule, and monitoring coverage depend on your service agreement, licenses, and configuration. Gamma can explain the protections in place and the next improvement that matters for your business, with a reporting route your staff can find quickly.
How Gamma uses INKY and BullPhish ID
INKY gives staff context inside the message
Gamma uses INKY email protection to help examine incoming messages for phishing and impersonation. INKY can place warning banners inside an email, giving employees context about concerns such as a suspicious link or unfamiliar sender.
Gamma configures the agreed protection and reporting route, then investigates messages your team flags. An INKY warning should prompt a pause and a report through that route. Payment changes still need independent confirmation through an established contact, even when a message has no warning.
BullPhish ID helps employees practice their response
Gamma uses BullPhish ID for security-awareness training and simulated phishing exercises. Short courses and practice emails help employees rehearse recognizing suspicious requests and reporting concerns before acting.
Gamma manages the agreed training program and reviews its results to identify where follow-up coaching would help. A finance team can apply those habits to a supplier requesting new bank details. Staff can pause the change, report the concern, and call an established contact before following the approval process.
Give payment changes a reliable verification step
The FBI recommends independently confirming payment changes, including changes in account numbers or procedures. Use a phone number already held in your approved supplier records, and treat contact details supplied in the request as unverified. A reply inside the same email conversation can reach the person controlling it.
Your finance process should identify who can approve a change and how the confirmation is recorded. A second authorized approver can help a busy team apply its own process consistently, especially during staff absences or urgent payment runs.
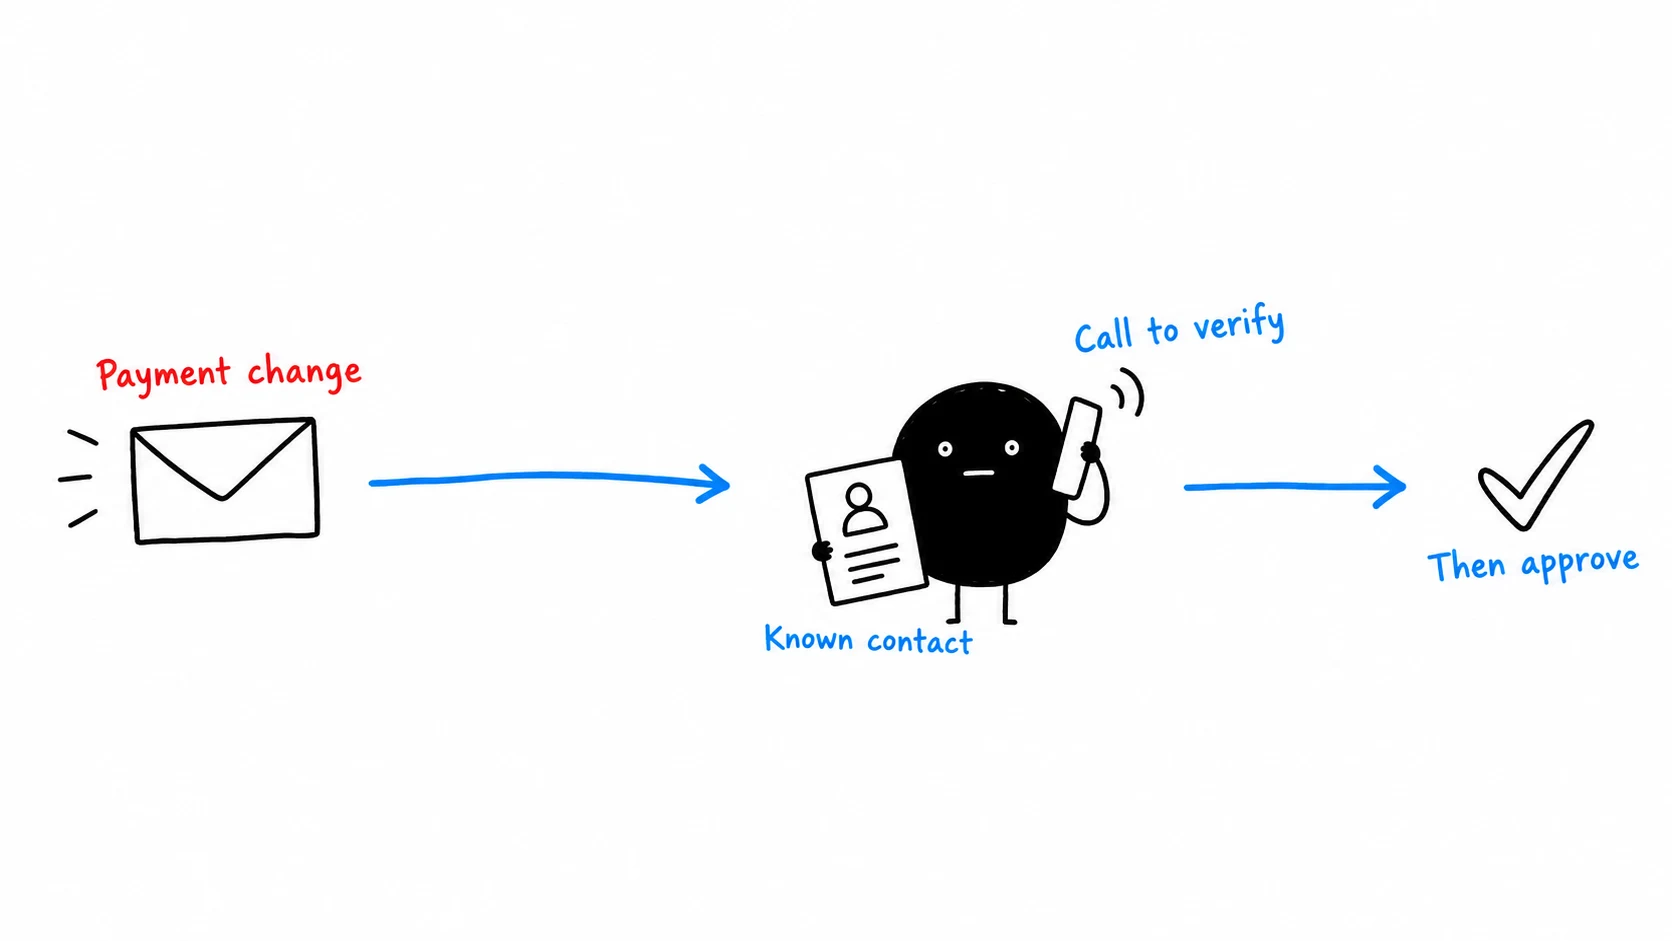
Open the illustration at full size.
A separate invoice problem also deserves attention: a convincing bill may describe services your business never ordered. The FTC’s invoice-scam guidance recommends clear purchasing and invoice approval procedures, with checks against vendors you actually use. Staff should compare the invoice with the approved purchase and contact the established supplier when something differs.
Use the payment-change planning sheet to agree on responsibilities before the next request arrives. Keep the completed sheet inside your business and use harmless sample information during practice.
- Name the person who can approve a supplier payment change and the backup during an absence.
- Identify where approved supplier contact records are maintained.
- Record how an independent confirmation and approval will be documented.
- Make Gamma’s established support contact available to the people handling payments.
- Practice a sample request without changing a live supplier record or sending money.
Get help quickly after a suspicious message or payment
An employee who entered a password, approved an unexpected sign-in, or noticed unusual mailbox activity should contact Gamma through the established support route promptly. Give the team a simple way to report the concern without fear of blame, because early reporting gives the investigation a useful starting point.
Microsoft’s compromised-account response guidance includes restricting access, resetting credentials, revoking active sessions, and examining forwarding rules and other account changes. Gamma can carry out the appropriate technical response within its authorized scope, investigate the affected mailbox, and help identify conversations that need follow-up. Recovery work depends on what the investigation finds, and a password reset alone may leave other unauthorized changes to address.
Money already sent requires immediate attention from your financial institution as well as technical help. Recovery is uncertain, so treat speed as important.
- Contact the bank immediately, explain the suspected fraud, and ask it to contact the receiving institution.
- Report business email compromise to the FBI’s Internet Crime Complaint Center.
- Keep the original message and transaction records available through secure channels.
Put the responsibility in place before the next payment run
A business owner should be able to name the team managing email security, the person approving payment changes, and the route for an urgent investigation. Gamma can review those handoffs with you and manage the agreed technical protections as part of your wider IT service.
Contact Gamma to review your business email protection, staff training, and response process, or call (239) 330-4939. We can connect the technical work with the way your staff actually handle supplier requests, customer commitments, and daily operations.